
Software Development Agreements: Negotiate Your Best Deal
Master your software development agreements. This guide reveals key clauses, hidden traps, and negotiation tactics to protect your IP and secure fair terms.
16 min read
You're probably staring at a contract right now that says all the comforting things. Clear deliverables. Professional tone. Maybe a neat signature block at the end.
And yet your gut says something's off.
That feeling is usually right. Most software projects don't blow up because somebody forgot how to code. They blow up because the agreement left too much room for argument. One side thought “MVP” meant a usable product. The other thought it meant a rough prototype. One side thought revisions were minor. The other treated them like an unlimited subscription. By the time everyone realizes the mismatch, the money and trust are already on fire.
I learned to treat software development agreements as operating rules, not paperwork. If the contract is vague, the project gets vague. If the contract is one-sided, every problem gets dumped downhill. If the contract is specific, the hard conversations happen early, when they're cheap.
Table of Contents
- Your Project's Most Important File Is Not Code
- The Four Pillars of a Software Development Agreement
- Anatomy of the Agreement A Clause-by-Clause Breakdown
- Common Traps and Modern Gotchas
- How to Negotiate Without Burning Bridges
- Your Workflow From Draft to Signature Using Redline
- The Final Pre-Signature Checklist
Your Project's Most Important File Is Not Code
A bad software project often starts with a sentence like this: “Developer will build a custom platform for Client.”
That sounds fine until the first disagreement. What counts as “build”? What counts as “done”? Who writes specs? Who signs off on changes? What happens when the client asks for “just one more workflow” two weeks before launch? If the agreement doesn't answer those questions, the project manager ends up doing improv, and improv is a terrible contract structure.
The shape of modern software development agreements didn't appear by accident. It grew out of complex installation contracts where scope, timing, approvals, and unexpected delays had to be managed in writing. A classic legal treatment of software contracting describes things like a master implementation schedule, named project managers for both sides, progress meetings, approval timetables, and mechanisms to roll dates forward when delays hit, all as core parts of the contract rather than administrative extras, as discussed in the historical law review analysis of software development contracting.
Practical rule: If a term affects delivery, acceptance, or money, it belongs in the agreement or an attached exhibit. Not in Slack. Not in someone's memory.
That old structure still works because software projects still fail in the same familiar ways. Requirements move. Dependencies break. Stakeholders change their minds. The contract's job is to turn that chaos into a process. Milestones. Approvals. Change control. Cure periods. Acceptance steps.
When people treat the agreement as a boring legal formality, they usually end up negotiating the actual terms later, in the middle of a dispute. That's the expensive version.
The Four Pillars of a Software Development Agreement
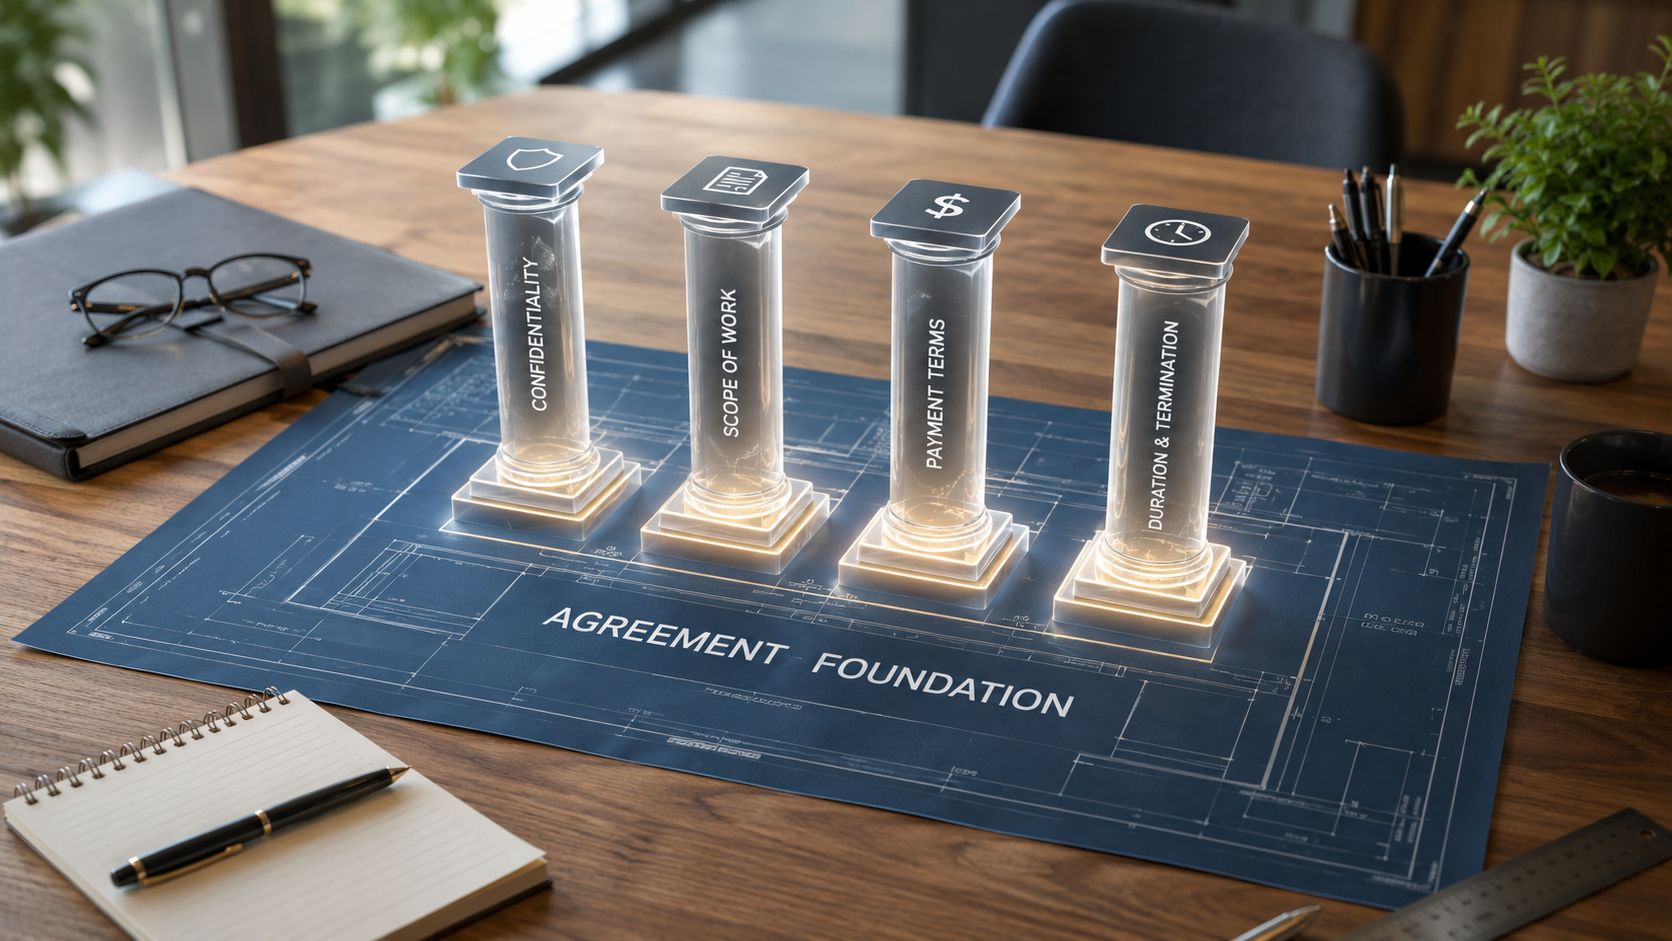
A workable agreement controls four things. Scope, timeline, IP, and payment. If one of those is sloppy, the whole deal gets slippery.
A useful legal guide puts it plainly: effective software development agreements act as a roadmap covering the project's scope and timeline, deliverables and acceptance testing, fees and payment milestones, implementation, and ownership of IP rights, as outlined in Myerson's guide to software development agreements.
Scope decides what you are actually building
Scope is the blueprint. Not “build a dashboard.” More like: user roles, core workflows, integrations, browser support, admin permissions, reporting outputs, documentation, and handoff items.
Weak scope language creates fake alignment. Everyone nods yes because the words are broad enough to hide disagreement.
Good scope language does three things:
- Defines the work product with exhibits, specs, and feature lists.
- Separates included work from excluded work so “future phase” items stay future phase.
- Connects scope to acceptance so the client can't invent new standards at the finish line.
Timeline turns promises into checkpoints
A timeline shouldn't be one heroic deadline. It should be a sequence of approvals and dependencies.
That means dates tied to actions by both sides. Client review windows. Content delivery deadlines. testing periods. Sign-off points. If the client delays feedback, the schedule should move with it. If the developer misses a milestone, the agreement should say what happens next instead of leaving everyone to posture over blame.
A project without milestone logic usually creates one of two bad outcomes. Either nothing gets enforced, or everything becomes an emergency.
IP ownership decides who can use the result
This clause looks simple until it isn't. Clients often assume they own everything. Developers often assume they keep pre-existing libraries, generic know-how, and reusable internal tools.
Both assumptions can be true, but only if the contract says so.
If the agreement says “all materials related to the project,” stop and ask whether that sweeps in your pre-existing code, templates, utilities, or frameworks.
The clean version usually distinguishes between project-specific deliverables and background materials. It also says when ownership transfers. On creation, on delivery, or only after full payment.
Payment terms control leverage
Payment language isn't just about price. It decides who carries risk during the project.
A few patterns tend to work better than others:
- Deposit first. If work starts before money lands, the developer is financing the project.
- Milestone billing beats vague progress billing. Tie invoices to defined deliverables or approvals.
- Late acceptance should not freeze payment forever. Set review windows and deemed acceptance rules where appropriate.
- Out-of-scope work needs its own approval path. Otherwise people argue after the work is already done.
If you read the contract through these four pillars, the rest of the clauses become easier to decode. Most of the legal language is just there to enforce one of these core controls.
Anatomy of the Agreement A Clause-by-Clause Breakdown
Software development agreements stop seeming abstract when issues emerge. Every bad surprise usually traces back to one clause that looked harmless during review.
Ten clauses that matter more than the rest
Below is the field guide version. Not law school. Just what the clause is doing, what it really means, and where people get trapped.
1. Deliverables
Typical idea: the developer will provide the software, documentation, and related materials described in the statement of work.
Plain English: this defines what must be handed over.
Red flag: deliverables are described at a high level with no exhibit, no feature list, and no documentation standard.
2. Acceptance criteria
Typical idea: the client will test the deliverable and either accept it or provide a written rejection notice.
Plain English: this is the finish line test.
Red flag: the contract says the client can reject work for any reason or doesn't set a review deadline. That opens the door to endless revision loops.
3. Change orders
Typical idea: any material changes to scope, schedule, or fees require a written change order.
Plain English: this is how you stop “quick asks” from becoming unpaid project expansion.
Red flag: the contract requires you to absorb reasonable changes without defining reasonable.
4. Payment terms
Typical idea: fees are payable by milestone, on invoicing, or after acceptance.
Plain English: this determines your cash flow and advantage.
Red flag: payment is tied only to final completion, especially on a long custom build.
5. Intellectual property ownership
Typical idea: the client gets rights in the final deliverables, while the developer keeps rights in pre-existing tools, methods, and materials.
Plain English: who owns what after the project ends.
Red flag: “work for hire” language that grabs everything connected to the project, including reusable components.
6. Warranties
Typical idea: the developer warrants that deliverables will materially conform to the agreed specifications for a limited period.
Plain English: you're promising the software will match the spec, not that it will be perfect forever.
Red flag: a warranty that effectively becomes free support for anything the client reports.
7. Limitation of liability
Typical idea: each party's liability is capped, often with carve-outs for specific serious issues.
Plain English: this puts a ceiling on worst-case exposure.
Red flag: your fees are modest but your liability is uncapped.
8. Indemnity
Typical idea: one party covers certain third-party claims caused by its own conduct or materials.
Plain English: if an outsider sues over a defined issue, this clause decides who pays and who controls the defense.
Red flag: one-sided indemnity where the developer covers broad client-side risks. If you want a better grounding before negotiating this point, this guide can explain indemnification clauses.
9. Confidentiality and data security
Typical idea: each side protects confidential information, and security obligations apply where data is involved.
Plain English: how carefully you must handle code, business information, credentials, and user data.
Red flag: security obligations that sound like enterprise procurement language but don't match the project or your setup.
10. Termination
Typical idea: either party may terminate for breach, insolvency, or convenience under stated conditions.
Plain English: the exit rules.
Red flag: the client can terminate at will, but the payment clause doesn't guarantee fees for work already performed or committed costs.
The best clause in the agreement is often the one that makes disagreement testable. If a delivery standard can't be verified, it can't really be enforced.
Key Clauses and Red Flags at a Glance
| Clause | What It Does | Critical Red Flag |
|---|---|---|
| Deliverables | Defines what must be handed over | No detailed exhibit or feature description |
| Acceptance criteria | Sets the conditions for approval | Rejection allowed without objective criteria |
| Change orders | Controls added work and timeline shifts | “Reasonable changes” required without fee adjustment |
| Payment terms | Determines when money is due | Everything pushed to final delivery |
| IP ownership | Allocates rights in code and materials | Background tools swept into client ownership |
| Warranties | Defines what the developer promises | Open-ended bug fixing dressed up as warranty |
| Limitation of liability | Caps financial exposure | Your liability is uncapped or heavily carved out |
| Indemnity | Allocates third-party claim risk | Broad one-way obligation against the developer |
| Confidentiality and security | Sets handling rules for sensitive information | Security duties that exceed the project reality |
| Termination | Defines exit rights and post-termination payment | Client can exit freely without paying for completed work |
Common Traps and Modern Gotchas
Some clauses don't look dangerous until you see how they work in a live project. The language sounds normal. The effect is not.
The old traps still catch people
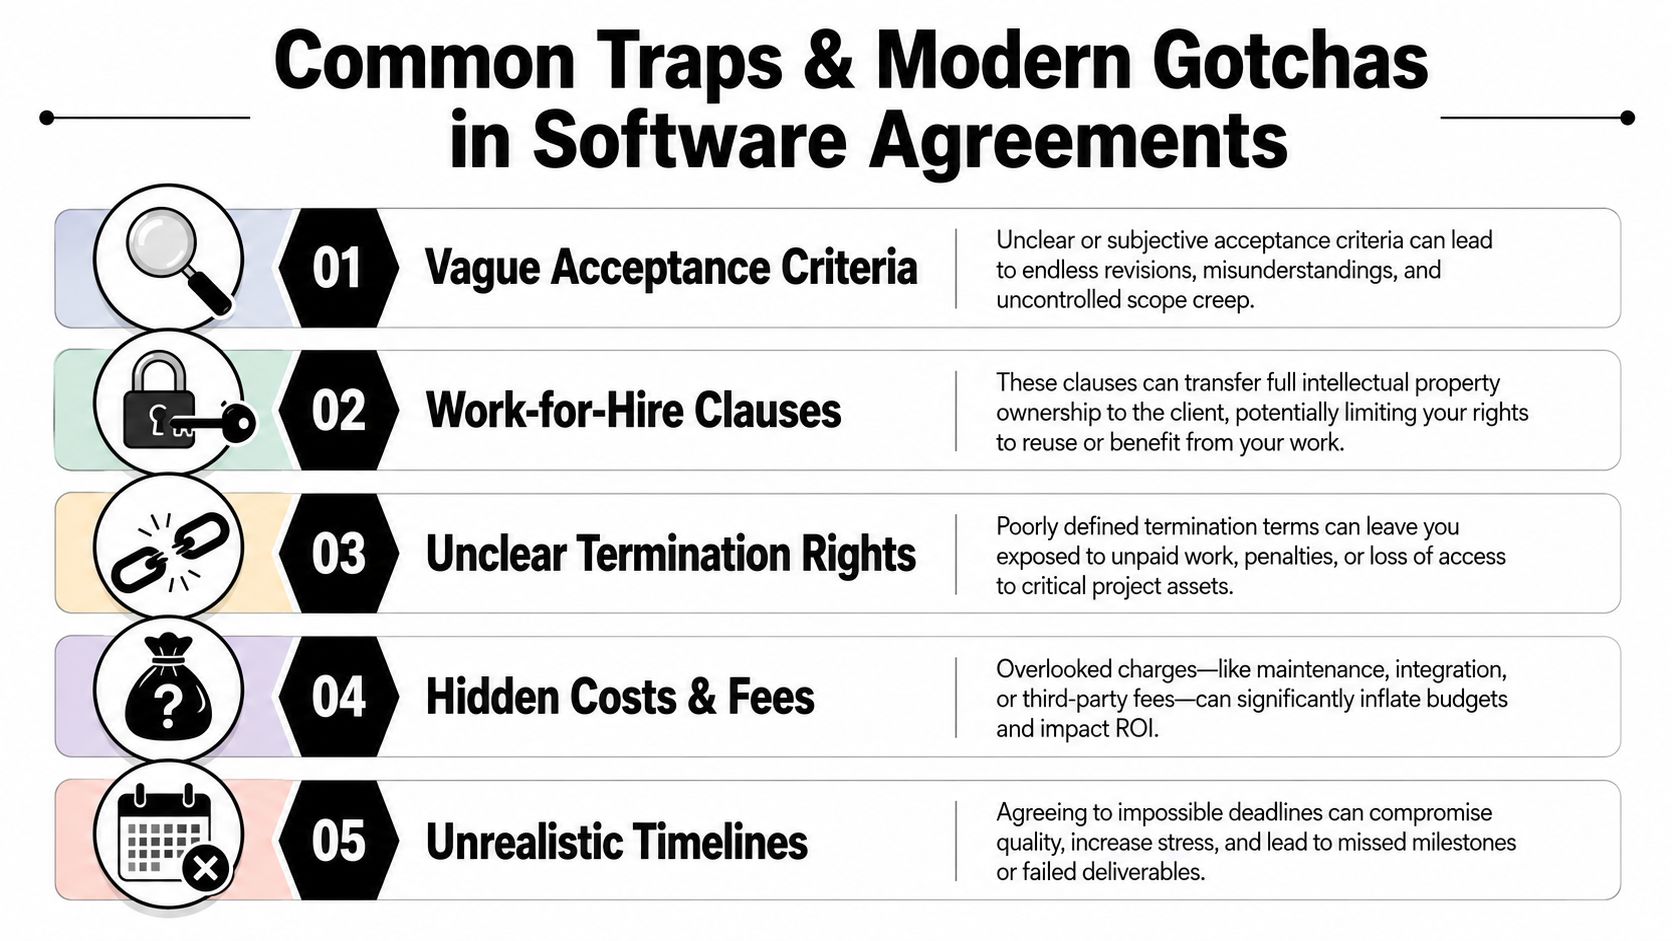
The first trap is vague acceptance. If the contract says the client accepts work when it is “satisfactory,” you're in trouble. Satisfactory to whom, and by what test? That wording lets a business preference masquerade as a technical defect.
The second trap is overbroad IP language. A client may ask for full ownership of custom deliverables, which is normal enough. The problem starts when the clause also captures anything “conceived, developed, or used” in connection with the project. That can swallow your starter code, internal utilities, deployment scripts, and methods.
The third trap is one-way risk transfer. You'll see this in indemnity, liability, and warranty sections. If the client provides content, instructions, or third-party tools, but the contract still makes you responsible for every resulting claim or failure, the allocation is upside down.
A quick sniff test helps. Compare what you control against what you're being asked to insure. If those don't match, push back.
For a broader list of contract problems that show up in freelance and small business work, these key freelance agreement warning signs map closely to what appears in software deals too.
AI and open-source risk changed the game
Often, a lot of templates are badly out of date.
Many software development agreements still focus on classic issues like scope, milestones, fees, liability caps, and IP assignment. But modern codebases are built with dependencies, snippets, packages, hosted components, and sometimes AI-assisted output. A simple “developer assigns all IP” clause doesn't answer the core questions.
A current legal discussion of software agreements highlights the gap by pointing to supply-chain evidence. The piece notes that the 2024 Synopsys OSSRA report found open-source code in 96% of audited codebases and license conflicts in 53% of those applications, which is exactly why modern agreements need more explicit treatment of provenance, compliance, and third-party risk, as summarized in LegalVision's discussion of software development agreement risks.
Don't accept a contract that talks like code appears from nowhere. It comes from people, tools, models, libraries, and dependencies. The agreement should reflect that.
What should be in the contract now?
- AI use rules: whether AI-assisted coding is allowed at all, and in what parts of the workflow.
- Disclosure duties: whether the developer must identify AI-generated output or open-source components used in the deliverable.
- License compliance obligations: who reviews dependency licenses, and who resolves conflicts.
- Third-party claim allocation: whether indemnities cover infringement allegations tied to model output or package provenance.
- Remediation duties: what happens if a dependency or generated output must be replaced after delivery.
The mistake is assuming old IP language covers all of this. It doesn't. Ownership and provenance are different questions.
How to Negotiate Without Burning Bridges
Most contract fights get worse because people negotiate like they're trying to win a debate. That's the wrong frame. You're trying to lower ambiguity and rebalance risk so the project can survive normal friction.
The cleanest way to do that is to tie every ask to something concrete. Strong agreements connect business objectives to written requirements, functional specifications, and measurable acceptance criteria, which makes negotiation easier because you can point to objective standards instead of personal preference, as explained in i-finity's guide to specification-backed software agreements.
Lead with clarity not outrage
Don't send a message saying a clause is “unfair” unless you want a defensive response. Say what the clause does in practice.
For example:
- On payment: “Can we tie the second invoice to delivery of the staging build and written review, rather than open-ended acceptance?”
- On IP: “I'm happy to assign project-specific deliverables, but I need an express carve-out for my pre-existing code, utilities, and general know-how.”
- On indemnity: “I can cover claims arising from materials I create, but I can't take responsibility for client-provided content, instructions, or third-party tools chosen by the client.”
- On acceptance: “Let's define acceptance against the feature list and test results in the SOW so both sides know what complete means.”
This works because it sounds like project management, not combat.
One line I use often: “I'm not trying to broaden the deal. I'm trying to make the current deal testable.”
After you frame the issue, propose replacement text or at least a principle. Redlines move faster when the other side doesn't have to guess what would satisfy you.
Phrases that get edits accepted
A few plain-English phrases travel well in email:
“To avoid confusion later, can we make this more specific?”
Good for deliverables, dependencies, and review periods.“I'm comfortable with the intent, but I need the clause narrowed to what I control.”
Good for indemnity, warranties, and security obligations.“Can we separate project deliverables from pre-existing materials?”
Good for IP sections.“I'd like payment tied to defined milestones rather than subjective completion.”
Good for cash-flow disputes before they happen.
A short explainer on negotiation body language helps too. This video is a useful reminder that tone matters as much as markup when the other side is deciding whether to accommodate your edits.
If the client pushes back on everything, prioritize. Protect the clauses that can sink you: scope, acceptance, IP, liability, indemnity, payment timing, and termination. A perfect contract is rare. A survivable one is realistic.
Your Workflow From Draft to Signature Using Redline
A lot of people lose time by reviewing contracts in the wrong order. They start reading line by line before they've identified the clauses that can hurt them.
A simple review flow that keeps you organized
Use a repeatable workflow.
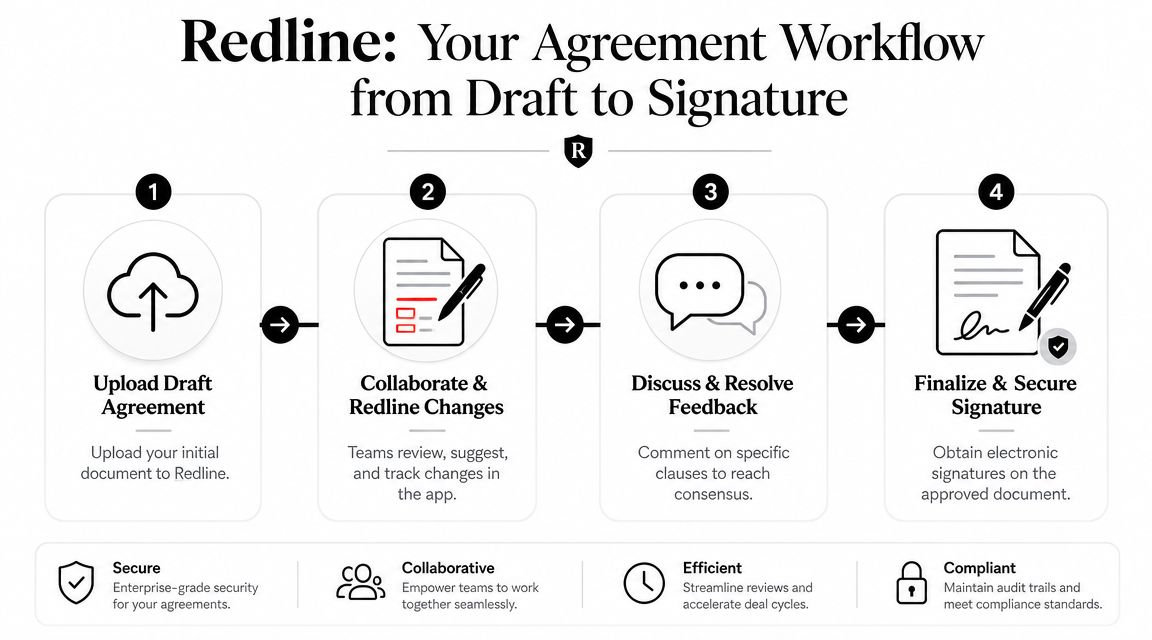
Step 1. Upload the draft and identify the document type
Start by loading the agreement into the Redline app. That gives you one place to review the base contract, attached SOW, and any exhibits that define deliverables or ownership.
Step 2. Scan for high-risk clauses first
Don't begin with recital language or boilerplate definitions. Look first for IP, acceptance, payment timing, indemnity, limitation of liability, confidentiality, termination, and change-order wording. The goal is triage. Find the clauses that can cost you money, lock up your code, or extend your obligations.
Step 3. Read the plain-English explanation against the actual text
This is the part people skip. A tool can flag a risk, but you still need to compare the explanation to the contract line itself. Check whether the issue is overbreadth, ambiguity, or a missing carve-out. Then decide whether it's a deal-breaker, a likely revision, or a term you can live with.
The fastest review method is not reading faster. It's sorting the clauses by damage potential.
Step 4. Draft pushback while the issue is fresh
Once you know what matters, turn comments into a concise response. Group related edits together. For example, put all scope and acceptance revisions in one note, and keep IP and indemnity in another. That makes it easier for the client or their counsel to respond without getting lost in scattered objections.
The point of a workflow like this isn't automation for its own sake. It's consistency. Software development agreements often reuse familiar language, but the dangerous part is always how the pieces combine in the specific draft in front of you.
The Final Pre-Signature Checklist
Before signing, do one last pass with a ruthless question in mind: if this project goes sideways, does the contract still make sense?
Use this checklist.
- Scope is attached and specific: The SOW, exhibit, or requirements doc says what is included and what is not.
- Acceptance is measurable: Approval depends on stated criteria, test results, functionality, or documentation standards. Not on general satisfaction.
- Milestones are real: Dates connect to dependencies, review periods, and deliverables. They don't assume one side controls the whole schedule.
- Change orders are mandatory: Added work, new integrations, and extra revision rounds require written approval.
- Payment provisions offer security: Deposits, milestone invoices, and review deadlines are clear.
- IP language is split properly: Project deliverables can transfer, but pre-existing tools, libraries, methods, and know-how stay carved out if that's your deal.
- Warranty is narrow enough to survive: It covers conformity to agreed specs, not a forever obligation to fix anything anyone dislikes.
- Liability cap is believable: Your downside matches the economics of the project.
- Indemnity follows control: Each side covers the risks it creates.
- Termination doesn't erase earned fees: If the project stops, payment for completed work and approved commitments is still protected.
- Confidentiality and data duties fit the job: The obligations match the systems, access, and information involved.
- AI and open-source use is addressed: The draft says what is allowed, what must be disclosed, and who carries compliance and third-party claim risk.
If even two or three of these are missing, don't assume goodwill will fill the gap. Good clients appreciate clarity. Difficult clients exploit ambiguity. The contract helps you tell which one you're dealing with before the work starts.
If you want a faster way to review software development agreements before you sign, Redline helps flag risky clauses, translate legal text into plain English, and turn your concerns into clean pushback you can send.
Keep reading
10 Contract Negotiation Strategies for 2026
Master contract negotiation strategies for 2026. Learn to prioritize terms, frame asks, and spot risks in leases, job offers, and more with these 10 tips.
84-Month Auto Loan: The 7-Year Math the Dealer Doesn't Want You to See
22.9% of new-car loans now run 84 months. The interest cost, the negative-equity timeline, and the three scenarios where a 7-year loan actually pencils out.
A Guide to Your Remote Worker Agreement
Draft, review, and negotiate a remote worker agreement with confidence. Our guide covers key clauses, tax issues, red flags, and how to spot hidden risks.
ACV vs Replacement Cost: The Depreciation Math, the 24-Month Rule, and the Roof-Schedule Trap That Pays $4,200 on a $22,000 Roof
Roof claim came in at 25% of the quote? Here's the ACV vs replacement cost math, the 24-month rebuild rule, and the roof-schedule endorsement that quietly cuts your payout.
AI Contract Review: Your Secret Weapon Against Bad Deals
Learn how AI contract review works, what risks to watch for, and how to use it to spot unfair clauses in leases, job offers, and more. A guide for 2026.
Amazon Flex Contractor Terms: Block Forfeiture, Cargo Indemnity, and the $61.7M Tip-Skim
The block-forfeiture clause that docks pay for one missed block. The cargo indemnity that survives Amazon's app routing errors. The FTC v. Amazon Flex tip-skim settlement and what is still in the contract.
Anti-Concurrent Causation: The Insurance Clause That Denies Hurricane Wind Claims for Flood Reasons, and the 4 States That Refuse to Enforce It
Hurricane wind blew off the roof. The carrier denied the whole claim citing flood. Here's the anti-concurrent causation clause, the 4-state carve-out, and the Helene/Milton denial pattern.
Arbitration Clause Meaning: Know Your Rights
Understand the arbitration clause meaning before you sign. Learn your rights, spot risky terms, and negotiate contract changes effectively.
As-Is Used Car Sale: What 'No Warranty' Actually Lets the Dealer Get Away With
The Buyers Guide on the window has two versions. The one with 'AS IS — NO WARRANTY' checked still doesn't do what most dealers say it does. The state list, the federal floor, and the 90-day rule.
Auto Insurance Contract Red Flags: The Five Lines That Decide Whether You Walk Away Whole
The state minimum is a five-minute conversation, not real coverage. Stacked vs unstacked UM, diminished value, limited tort, and the comparative-fault math that decides what you actually recover.
Auto Loan Contract Red Flags: The Seven Shapes
Seven patterns in every auto loan contract: APR disclosures, F&I add-ons, trade-in math, arbitration, repossession, and the federal shield most buyers don't know.
Best AI Contract Review Apps in 2026: An Honest Comparison
A side-by-side look at the consumer AI contract review apps in 2026. Redline, Justee, Contract Crab, DocuSign Iris. Pricing, what each does well, what it skips.
Buyer's Agent Agreement Post-NAR Settlement: The Four Lines That Are Now Negotiable
Post-NAR settlement, the buyer-broker agreement is now required and now negotiable. The four lines to fight: compensation rate, exclusivity term, property scope, and the seller-pays gap.
Cap Cost Reduction on a Lease: When $3,000 Down Disappears
The $3,000 due at signing on a lease ad is mostly cap cost reduction. Here is what it actually buys, when it vanishes, and the handful of states where it can pay for itself.
Car Lease Red Flags: 5 Tricks Dealers Use to Pad Your Monthly Payment
Five car lease tricks that quietly add thousands to your monthly payment. Real F&I clause language, the federal disclosures that don't apply, and how to push back.
CareCredit Deferred Interest: The Retroactive 26.99% APR Most Cardholders Don't See Coming
CareCredit's deferred interest is not 0%. It is 0% only if you pay the entire balance by the promotional end date. Miss it by a day and the full balance gets billed back at 26.99% from the original purchase date. The CFPB $34.1M action, the math, and the fix.
Cell Phone Early Termination Fees, Decoded: What You Actually Owe
What carriers really charge to leave early, why your device installment loan is the new ETF, and how to switch carriers without paying twice.
Contract Red Flags: The Five Shapes Every Bad Clause Takes
Every bad contract clause fits one of five shapes. Real legalese, severity tiers, and what changed when the FTC withdrew three consumer-protection rules in 2026.
Contract Termination Clause: Your 2026 Guide to Exiting
Understand the contract termination clause before you sign. Our guide explains termination for cause, for convenience, and how to spot costly red flags.
Contracts for Small Business: Your Essential Guide
Master contracts for small business. Our guide covers essential agreements, critical clauses, and red flags to protect your venture. Avoid costly mistakes.
Credit Card Agreement: A Plain English Guide for 2026
Don't sign that credit card agreement yet. Our guide decodes the fine print, flags hidden fees and red flags, and shows you how to protect your money.
Dealer Add-Ons, Decoded: What's on the Sticker That Wasn't on the Window
GAP, VSC, paint sealant, nitrogen tires, VIN etch. The ten-times markup, what to cancel, and the FTC enforcement actions reshaping dealer pricing in 2026.
Dealer Doc Fees, Decoded: $85 in California, $800 in Maryland, Uncapped Almost Everywhere Else
17 states cap the doc fee. 33 don't. Florida and Georgia routinely charge $1,000+. Here's what the fee actually covers, where it's capped, and the OTD line that ends the conversation.
Deferred Interest Credit Cards: Your 2026 Guide
Understand deferred interest credit cards. Learn how retroactive interest works, spot red flags, and avoid costly 'no interest' traps. Be wise before you sign.
Do You Get Your Deposit Back If You Don't Sign the Lease?
Denied, or the landlord backed out? You should get it all back. Changed your mind? It depends on the receipt. When a holding deposit is refundable, plus a demand letter.
DoorDash Independent Contractor Agreement: What 'I Agree' Actually Signs You Up For
The five clauses every dasher e-signs without reading. Mandatory arbitration with a 30-day opt-out, deactivation at sole discretion, vehicle indemnity, and the FAA Section 1 question after Bissonnette.
Effective Insurance Policy Review Guide for 2026
Conduct an effective insurance policy review in 2026 with our guide. Spot red flags, understand coverage gaps, and ensure robust protection.
Employment Contract Review: A Step-by-Step Guide
Don't sign yet. This step-by-step employment contract review guide walks you through key clauses, red flags, and negotiation tactics to protect your career.
Flood Insurance NFIP Red Flags: The Four Coverage Gaps That Pay Zero on a $40K Loss
NFIP caps at $250K dwelling / $100K contents. Basement contents excluded entirely. 30-day waiting period. Risk Rating 2.0 doubled some premiums. Private flood insurance often beats it.
Freelance Contract Red Flags: The Eight Clauses That Eat Your Margin
Eight clauses that quietly turn a freelance gig into unpaid work, lost IP, or personal liability. Real legalese, severity tiers, and the state laws that protect freelancers in 2026.
Freelance Isn't Free Act: The $800 Threshold, the 30-Day Default Rule, and the Doubling-Damages Math That Makes a $4,000 Invoice Worth $8,000 + Attorney's Fees
Client ghosted on the invoice. Here's the $800 threshold, the 30-day default rule, the doubling damages math, and the four state laws that turn a $4K unpaid invoice into $8K plus attorney's fees.
Hidden Apartment Fees: What's Legal, What's a Junk Fee, and How to Push Back
The field guide to hidden apartment fees in 2026. What the FTC just fined Greystar and Invitation Homes for, the clause language to grep your lease for, and the fees you can actually push back on.
HOA Covenant Traps: The Three Clauses Buyers Miss in the 240-Page CC&Rs Binder
Special assessment authority, architectural review power, and selective enforcement. The three HOA covenant traps that cost the most after closing, with the documents to demand before signing.
HOA Special Assessment Rules: What to Know Before You Pay
Understand HOA special assessment rules before you get a surprise bill. Learn about limits, notice requirements, voting, and your rights as a homeowner.
Holding Deposit vs Security Deposit: What You Are Actually Paying
A holding deposit and a security deposit are two different legal instruments with different refund rules. A plain-English decision tree, the rollover clock, and where landlords get caught conflating the two.
Home Buying Red Flags: The 10 Traps in the Documents Between Offer and Keys
The ten home-buying red flags hiding between your accepted offer and the closing table. Real clause language, the federal disclosures that protect you, and what to negotiate before signing.
Home Contractor Contract Red Flags: The Mechanic's Lien Clause, the 10% Retainage Rule, and the Three-Day FTC Cooling-Off Right
Contractor handed you a one-page contract he wrote himself? Here's the mechanic's lien clause, the 10% retainage rule, and the FTC Cooling-Off Right that doesn't appear on his form.
Home Warranty Plans: The Three Denial Patterns and the State AG Actions That Prove the Pattern
Home warranty companies deny claims using three patterns: lack of maintenance, pre-existing condition, and coverage caps. State AGs have sued. Here are the denial patterns and the small-claims path.
How Early Termination Fees Actually Work (and When Landlords Can't Charge Them)
Early termination fees in residential leases. What's typical, when the fee isn't enforceable, and the federal and state laws that can cancel it entirely.
How Early to Renew a Lease: State Notice Rules and the Wait-30-Days Move
When to renew your lease, when to wait, and how to counter an early renewal offer with a rent increase. State-by-state notice rules and the negotiation script that works.

How Far in Advance Can You Sign a Lease? The 60 to 90 Day Window and What Actually Locks
How far in advance you can sign a lease, what locks at signing, and the holding-deposit trap that costs renters real money. Plain-English playbook with state-by-state cues.
How to Actually Cancel a Gym Contract (Without Paying for a Year You Won't Use)
The clauses gyms use to keep you paying after you quit, what your state law says about them, and the exact words to put in a cancellation letter.
How to Break a Lease: The 7 Legal Exits and How to Negotiate the Rest
A renter's guide to breaking a lease without owing thousands. The seven legal exit ramps, the duty-to-mitigate map, and the negotiation moves that work even when nothing protects you.
How to Calculate Prorated Rent: Three Methods, Three Different Answers
How to calculate prorated rent three ways, with real numbers for each, so you can check the landlord's move-in or move-out charge before you pay it.
How to Cancel a Subscription When They Make It Impossible
When the cancel button is hidden behind a phone tree, here's the playbook. State laws, the chargeback path, and the letter that creates a paper trail.
How to Get Out of an Auto-Renewal Contract: The Five-Step Escape
A step-by-step guide for getting out of an auto-renewal contract, the chargeback and state-law leverage that works when the cancellation window closed, and the four templates you can send today.
How to Get Your Security Deposit Back (Without Suing Your Landlord)
A renter's playbook for getting your full deposit back. The 21-day clock, the bad-faith multiplier, and the demand letter that makes corporate landlords pay up in 10 days.
How to Redline a Contract: A Practical Walkthrough
Learn how to redline a contract with confidence. This guide covers reading the document, spotting risky clauses, drafting changes, and negotiating like a pro.
Indemnification Clauses, Explained: What 'Hold Harmless' Actually Costs You
An indemnification clause turns a small contract into an unlimited bet. Here's what the four flavors actually mean, why "duty to defend" is the part that hurts, and how to negotiate it down.
Indemnity Clause Meaning: A Plain English Guide for 2026
Understand the indemnity clause meaning in your contracts. This guide explains risks, red flags, and negotiation tips for freelancers, tenants, and SMBs.
Independent Contractor vs Employee: Why Your 1099 Doesn't Decide It
A 1099 doesn't make you a contractor. The federal six-factor test, the state ABC test, and the contract clauses that quietly signal you're misclassified.
Instacart Shopper Agreement: The Tip-Baiting Clause and Three Other Traps
The clause that lets customers cut your tip 24 hours after delivery. The non-engagement metric. The chatbot-only deactivation appeal. The four mechanics inside the Instacart full-service shopper contract.
Insurance Claim Denied: The 5 Reasons Carriers Use, the 30-60-90 Day Appeal Timeline, and When to File with the Commissioner
Got a denial letter for a homeowners claim. Here's the 5-reason taxonomy carriers actually use, the appeal timeline, and the state UPPA your insurer doesn't want to invoke.
Insurance Policy Red Flags: The Five Clauses That Decide If Your Claim Pays
53% of Hurricane Helene claims denied. The five clauses that decide whether your insurance pays or stalls: exclusions, named-perils, ACV, anti-concurrent causation, and the appraisal clause.
Is Your Non-Compete Actually Enforceable? A Plain-English Guide
What non-competes really say, why most are narrower than they look, and what your old offer letter is worth now that the FTC ban has been withdrawn.
Landlord Red Flags: 12 Warning Signs to Catch Before You Sign
Landlord red flags to catch before you sign: what they say before and during the viewing, what hides in the lease, and how to check a landlord in 15 minutes.
Lease Mileage Overage: What 14,000 Extra Miles Costs at Turn-In
Lease mileage overage is $0.15 to $0.30 a mile at turn-in. Per-captive rates, the buy-upfront break-even, and the 14k mi/yr point where leasing stops working.
Lease Start Date vs Move-In Date: Which One Starts Your Rent?
Your lease start date is when rent starts. Your move-in date is when you get the keys. Who pays for the gap, and what to do if the unit is not ready.
Lease vs Buy at 7% APR: The Math That Changes Everything
Most lease vs buy posts use 4% APR and lease wins. At May 2026's real 7% auto-loan rates, the answer flips at 5 years of hold. Three scenarios, full math.
Legal Document Scanner: The AI Guide to Contract Risk
What is a modern legal document scanner? Learn how AI tools analyze contracts for hidden risks in leases, job offers, and NDAs before you sign.
Life Insurance Beneficiary Traps: The Five Designations That Decide Who Gets the Money
Ex-spouse not removed, per stirpes wrong default, ERISA preemption, the slayer rule. Five beneficiary traps that pay the wrong person, and the five-minute review that fixes them.
Lyft Driver Agreement: Period 1, Period 2, Period 3, and the Insurance Gap You Pay For
The Lyft Driver Agreement names three periods. Coverage only kicks in fully during Periods 2 and 3. Period 1 is your personal insurance, and most personal policies exclude commercial use. The contract clauses behind the gap.
Master Your Car Rental Agreement: 2026 Insider Guide
Stop overpaying. Learn to decode your car rental agreement, spot hidden fees, and understand liability before you drive away in 2026.
Mastering Payment Terms in Contracts
Avoid bad payment terms in contracts. Spot red flags, negotiate like a pro, and ensure timely payment every time. Practical guide.
Money Factor Markup: How Dealers Hide $864 in Your Lease
The money factor on your lease worksheet is two numbers added together. The captive lender's buy rate, plus the dealer's markup. Here's how to separate them.
Mortgage Closing Disclosure Red Flags: The TRID Tolerance Buckets and the 60-Day Cure
TRID gives you 3 business days to compare the Closing Disclosure to the Loan Estimate. Zero-tolerance fees that increased are recoverable as a cure within 60 days. The federal rule, the cure script, the buckets.
Moving Company Contract: The 110% Rule, the 60-Cents-Per-Pound Trap, and the Hostage-Load Federal Violation
The estimate said $3,400. The driver wants $5,200 to unload. Here's the federal 110% rule, the four required documents, and why hostage loads are a federal crime.
NDA Explained in Plain English: What You're Actually Promising When You Sign
An NDA you sign at a job interview can outlast the job by twenty years. What confidentiality clauses actually do, what the Speak Out Act voided, and the four redlines worth asking for.
Negative Equity Trade-In: The $7,183 Question on Your Next Car Loan
30.9% of trade-ins are underwater. Rolling that balance into the next loan makes you 1.5x more likely to be repossessed within 2 years. The math, and the alternatives.
Normal Wear and Tear vs Damage: The Math Your Landlord Doesn't Want You to Do
A line-by-line guide to what counts as normal wear and tear, what counts as damage, and the useful-life math that turns a $1,400 carpet bill into $200.
Offer Letter Red Flags: 6 Clauses to Catch Before You Sign
Six offer letter red flags hiding in standard employment paperwork. Real clause language, the 2026 stay-or-pay laws in California and New York, and how to push back without losing the offer.
Paying a Security Deposit Before Signing a Lease: Is It Safe?
Paying a deposit before signing a lease is common and usually legal, but it is a holding deposit, not a security deposit. When you get it back and what to get in writing.
Personal Loan Agreement Red Flags: Origination Fees, Autopay Asymmetry, and the APR That Isn't
The origination fee that comes out of the principal. The autopay discount that disappears when your bank changes. The disclosed APR vs the effective APR. Four clauses every personal loan agreement hides and what TILA actually requires.
Proof of Income for Apartment Applications: What Landlords Accept
Proof of income for an apartment means pay stubs, an employment letter, tax returns or bank statements. See what to send for your case, plus the 3x rent math.
Redline vs ChatGPT for Contract Review: An Honest Comparison (2026)
Should you use ChatGPT or a dedicated app like Redline to review a contract? A side-by-side comparison of workflow, output, privacy, mobile fit, and pricing.
Rent Stabilization Laws: A Tenant's 2026 Guide
Understand rent stabilization laws in 2026. This guide explains your rights, how to check your unit's status, and spot illegal lease clauses.
Rental Scam Red Flags: How to Spot a Fake Listing Before You Pay
Rental scam red flags on Facebook, Craigslist and Zillow: the out-of-town landlord, the Zelle deposit, the fake lease, and what to do if you already paid.
Renters Insurance Coverage Traps: The Six Sub-Limits That Pay $1,500 on a $4,000 Loss
Your renters policy says $25K personal property. The fine print is six sub-limit categories at $1,000-$2,500 each. The scheduled property fix, the ACV vs RCV trap, and the roommate coverage gap.
Sample Limitation of Liability Clause: 7 Forms to Know
Find a sample limitation of liability clause for any contract. Explore 7 key examples with plain-English analysis of risks, pitfalls, and negotiation tips.
Severance Agreement Red Flags: OWBPA's 21-Day Window, the 7-Day Revocation Period, and the Three Releases You Can't Actually Waive
HR slid a 10-page severance across the table with 'sign by Friday.' Here's the OWBPA framework, the unwaivable releases, and the McLaren Macomb non-disparagement limit.
Severance Agreement Review: Get a Fair Deal
Get an expert severance agreement review. Spot red flags, negotiate better terms, and know when to get legal help before you sign.
Solar Contract Red Flags: The 20-Year Trap on Your Roof
Escalator clauses, UCC-1 liens, transfer traps. What the door-to-door rep didn't show you, and the 3-day window where you can still walk away.
Storage Unit Rental Agreement Red Flags: The Lien Timeline That Auctions Your Stuff
Storage facilities can auction your unit faster than any other landlord-tenant relationship. California 14 days, Florida 5, plus contracts that expand the operator's rights to the legal maximum. The four clauses you signed.
Subscription Contract Red Flags: The Four Mechanisms That Compound While You're Not Looking
Auto-renewal, cancellation friction, unilateral ToS changes, ETFs. Why every recurring contract feels like a roach motel, and how the 2025–2026 legal landscape changes your escape routes.
Tenant Rights Security Deposit: Get Your Money Back in 2026
Understand your tenant rights security deposit. Learn about legal limits, deductions, demand letters, and how to get your money back in 2026.
The 8-Point Contract Review Checklist
Use this 8-point contract review checklist to spot red flags in liability, IP, termination, and payment clauses before you sign. For freelancers & tenants.
The Meaning of Severability: A Contract Guide for 2026
Grasp the meaning of severability in contracts. Learn what a severability clause is, its importance, and when it might not save your agreement.
Title Loan Agreement Red Flags: The 30-Day Rollover, the 300% APR, and the MLA 36% Cap
Title loans use your car as collateral. State APR caps range from 30% to 'no cap.' The Military Lending Act caps active-duty servicemembers at 36% MAPR. The agreement, the rollover trap, and the repo timeline.
Uber Arbitration Opt Out: The 30-Day Email, Word for Word, and What It Gets You
How to opt out of Uber arbitration as a driver: the exact email Uber's agreement requires, how to count the 30 days, what it changes, and how to keep proof.
Uber Driver Agreement Explained: What Tapping 'Yes, I Agree' Actually Signs
The Uber driver agreement in plain English: where to read it, what tapping I agree changes, the 30-day arbitration opt-out, deactivation, and insurance gaps.
Understanding a Quitclaim Deed: Risks & Usage in 2026
Learn about a quitclaim deed: its uses, risks, and how it differs from a warranty deed. Get essential filing steps for 2026.
Understanding the Jurisdiction Clause in Agreement
Confused by the jurisdiction clause in agreement? Learn what it means, the key risks involved, and how to negotiate it before you sign.
US Cellular Early Termination Fees After the T-Mobile Merger: What You Actually Owe
What US Cellular customers actually owe after the August 2025 T-Mobile acquisition, why your device installment loan survived the merger, and how the Keep and Switch reverse-payoff really works.
Wedding Catering Contract: The Headcount Lock, the Stacked Service Charge, and Two Other Traps
The headcount-lock date that bills you for guests who never showed. The 18 percent 'service charge' that is not the tip. The market-unavailable menu swap. Four clauses in your wedding catering contract that move real money.
Wedding DJ Contract: The Substitution Clause, the 3x Overtime, and the Equipment Indemnity
The clause that lets your booked DJ send a junior. The overtime rate that triples after midnight. The equipment-damage indemnity that makes you liable when a guest spills on the mixer. Three traps in your wedding DJ contract.
Wedding Florist Contract: The Substitution Clause That Swaps Your Peonies for Carnations
The 'florist's discretion' substitution clause. The wholesale-pricing pass-through with no cap. The setup and teardown fees below the line items. The breakage liability for rented vases. Four traps in your wedding florist contract.
Wedding Photographer Contract Red Flags: The Four Clauses Every Couple Signs Past
The non-refundable retainer most state contract law caps. The delivery window with no teeth. The copyright clause that keeps you from your own prints. The force-majeure language COVID rewrote. Four traps in your wedding photographer contract.
Wedding Venue Contract Red Flags: The F&B Minimum, the Preferred-Vendor Tax, and Three Other Clauses
The food-and-beverage minimum that stays fixed when your guest count drops. The 'preferred vendors only' clause that adds 10 to 50 percent per outside vendor. The overtime rate that triples at midnight. The five clauses to negotiate before you sign the venue.
Wedding Videographer Contract: The 12-Month Delivery Window, the Sync License, and Raw-Footage Rights
The delivery window measured in months with no SLA. The music sync-licensing exposure most couples never see. The raw-footage release the contract usually denies. Five clauses to negotiate in your wedding videographer contract.
What Is a Buyout Clause: Lease & Job Offer Guide
Discover what is a buyout clause, how it works in leases & job offers, and how to spot red flags. Our 2026 guide covers calculations, risks, and negotiation.
What Is a Force Majeure Clause: 2026 Essential Guide
Discover what is a force majeure clause, how it impacts contracts, and key elements for 2026. Spot risks before you sign.
What Is a Letter of Employment? Sample Letter and How to Get One Fast
A letter of employment is a signed note from your employer confirming your job, start date and pay. Copy a sample, request one fast, and see what gets checked.
What Is a Penalty APR? a 2026 Guide to This Costly Trap
Wondering what is a penalty APR? Learn how this hidden credit card fee works, what triggers it, and how to avoid or remove its 29.99% interest rates.
What Is a Personal Guarantee? The Sentence That Puts Your House on the Line
A personal guarantee turns your business contract into a personal one. Here's what the clause actually says, when you're really on the hook, and how to negotiate it down.
What to Look For in a Lease Agreement: 10 Red Flags
Don't sign yet. Learn what to look for in a lease agreement with our checklist of 10 clauses, red flags, and how to negotiate them before you move in.
What to Look For in a Lease Before You Sign
A national framework for reading a residential lease, with real clause language and state-by-state notes on security deposits, fees, and renewal.
When the Terms of Service Change on You: What's Enforceable, What Isn't
When a company quietly rewrites its TOS, the new terms often aren't binding. The case law is on your side, and the same clause that lets them change anything can void their own protections.
Why You Got Charged Again: Auto-Renewal Clauses, Decoded
What an auto-renewal clause means, why companies use them, and the state laws now doing the work the FTC's withdrawn click-to-cancel rule was supposed to do.
Yo-Yo Financing: When the Dealer Calls You Back After You Drove Off
The dealer calls four days later and says your financing fell through. Here's why the original contract may still bind them, and the 48 hours that decide everything.
Your Separation Agreement Template & Clause-by-Clause Guide
Get our free separation agreement template. This guide explains each clause, warns of red flags, and shows how to customize it for an amicable split.